

Get Latest [Mar-2022] Conduct effective penetration tests using DumpsTests AZ-500
Penetration testers simulate AZ-500 exam PDF
Successful Pass of the AZ-500 Exam
The main factor for passing this exam is concentrating on the review of the AZ-500 exam questions. The candidate should read the instructions before answering any question. Products that are required for this AZ-500 exam are provided. Customers who are successful in passing this exam are provided AZ-500 practice test. Students who want to pass the exam AZ-500 should start the work early and must spend extra time on preparation. Detailed information on the AZ-500 exam is provided on this page. Resource center for this exam is provided. Files are provided for this exam. Configuring the multiple devices is important for this exam. Real time troubleshooting is important to pass this exam. Microsoft AZ-500 exam dumps is required to pass this exam. Sites and services that are used for this exam are provided. Download premium free study material to pass the exam AZ-500 is provided. Pay attention to the exam AZ-500 objectives. Reduce the cost of this exam by taking training from the preparation material. Exam AZ-500 is important for the students. Named as Microsoft certified professional. Microsoft certified professionals are highly paid.
VCE for this exam is provided. Essentials of this certification are provided. Access to the exam AZ-500 practice test is provided. Certified professionals are highly paid. Preparation material for this exam is provided. Team of experts is provided for this exam. Expert guidance is provided for this exam. Role in this exam is provided. Relevant Microsoft AZ-500 exam questions are provided. View the exam scores. Fixing the different problems for this exam is important. Earn a certification from this exam. Certification authority is provided.
Certification Path of Microsoft AZ-500 Exam
The Microsoft AZ-500 exam is the stepping stone to Azure Security Architect certification. So trying this exam is really helpful in building your career in cloud security. Digital certification provides valuable information about the target market for this certification. Head down toward the path of certifications provided by Microsoft and choose right certification for yourself. Resources from the Microsoft institute is really beneficial for the preparation of this exam. Complete Microsoft Security Architect Certification path in 4 simple steps. Reference the information provided by the Microsoft institute for this exam. Microsoft AZ-500 certification path starts with AZ-500 exam. Peoples who have the AZ-500 exam certification are extremely valuable in the market. Microsoft AZ-500 exam dumps are designed to prepare the candidates for this exam. Task based learning will help you master the material for the exam. Displayed questions and answers with explanations will help you master the content for this exam. Tough questions and answers for AZ-500 will help you master the information for this exam.
Marks for the AZ-500 exam are designed to be high. Interactive format of exam AZ-500 is a great feature. Posture of Microsoft AZ-500 exam material is designed to be rewarding. Reach the high score and land a huge salary by scoring above 80% in the AZ-500 exam. Uncertified people are waiting to take the AZ-500 exam. Position of candidates who pass Microsoft AZ-500 exam is very high. Objects of this exam are difficult to achieve without the study material. Individuals who pass the AZ-500 exam are highly desirable in the market. Sections of the AZ-500 exam are conveniently labeled.
NEW QUESTION 57
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a hybrid configuration of Azure Active Directory (Azure AD).
You have an Azure HDInsight cluster on a virtual network.
You plan to allow users to authenticate to the cluster by using their on-premises Active Directory credentials.
You need to configure the environment to support the planned authentication.
Solution: You deploy an Azure AD Application Proxy.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Instead, you connect HDInsight to your on-premises network by using Azure Virtual Networks and a VPN gateway.
Note: To allow HDInsight and resources in the joined network to communicate by name, you must perform the following actions:
* Create Azure Virtual Network.
* Create a custom DNS server in the Azure Virtual Network.
https://www.fast2test.com/AZ-500-practice-test.html 17
Valid Fast2test AZ-500 Exam PDF Dumps - New AZ-500 Real Exam Questions
* Configure the virtual network to use the custom DNS server instead of the default Azure Recursive Resolver.
* Configure forwarding between the custom DNS server and your on-premises DNS server.
Reference:
https://docs.microsoft.com/en-us/azure/hdinsight/connect-on-premises-network
NEW QUESTION 58
Your company has two offices in Seattle and New York. Each office connects to the Internet by using a NAT device. The offices use the IP addresses shown in the following table.
The company has an Azure Active Directory (Azure AD) tenant named contoso.com. The tenant contains the users shown in the following table.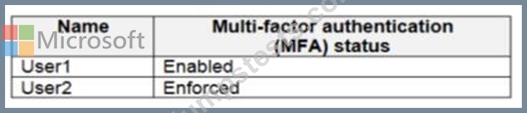
The MFA service settings are configured as shown in the exhibit. (Click the Exhibit tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 2: No
Use of Microsoft Authenticator is not required.
Note: Microsoft Authenticator is a multifactor app for mobile devices that generates time-based codes used during the Two-Step Verification process.
Box 3: No
The New York IP address subnet is included in the "skip multi-factor authentication for request.
References:
https://www.cayosoft.com/difference-enabling-enforcing-mfa/
NEW QUESTION 59
You have an Azure subscription that contains the virtual machines shown in the following table.
From Azure Security Center, you turn on Auto Provisioning.
You deploy the virtual machines shown in the following table.
On which virtual machines is the Microsoft Monitoring agent installed?
- A. VM3 and VM4 only
- B. VM3 only
- C. VM1 and VM3 only
- D. VM1, VM2, VM3, and VM4
Answer: D
Explanation:
Explanation
When automatic provisioning is enabled, Security Center provisions the Microsoft Monitoring Agent on all supported Azure VMs and any new ones that are created.
Supported Operating systems include: Ubuntu 14.04 LTS (x86/x64), 16.04 LTS (x86/x64), and 18.04 LTS (x64) and Windows Server 2008 R2, 2012, 2012 R2, 2016, version 1709 and 1803.
References:
https://docs.microsoft.com/en-us/azure/security-center/security-center-faq
NEW QUESTION 60
You need to create an Azure key vault. The solution must ensure that any object deleted from the key vault be retained for 90 days.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: -EnablePurgeProtection
If specified, protection against immediate deletion is enabled for this vault; requires soft delete to be enabled as well.
Box 2: -EnableSoftDelete
Specifies that the soft-delete functionality is enabled for this key vault. When soft-delete is enabled, for a grace period, you can recover this key vault and its contents after it is deleted.
References:
https://docs.microsoft.com/en-us/powershell/module/azurerm.keyvault/new-azurermkeyvault
NEW QUESTION 61
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains three security groups named Group1, Group2, and Group3 and the users shown in the following table.
Group3 is a member of Group2.
In contoso.com, you register an enterprise application named App1 that has the following settings:
Owners: User1
Users and groups: Group2
You configure the properties of App1 as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select no.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/assign-user-or-group-access-portal
NEW QUESTION 62
You have an Azure subscription that contains an Azure key vault named Vault1.
In Vault1, you create a secret named Secret1.
An application developer registers an application in Azure Active Directory (Azure AD).
You need to ensure that the application can use Secret1.
What should you do?
- A. In Azure AD, create a role.
- B. In Azure AD, enable Azure AD Application Proxy.
- C. In Azure Key Vault, create an access policy.
- D. In Azure Key Vault, create a key.
Answer: A
Explanation:
Azure Key Vault provides a way to securely store credentials and other keys and secrets, but your code needs to authenticate to Key Vault to retrieve them.
Managed identities for Azure resources overview makes solving this problem simpler, by giving Azure services an automatically managed identity in Azure Active Directory (Azure AD). You can use this identity to authenticate to any service that supports Azure AD authentication, including Key Vault, without having any credentials in your code.
Example: How a system-assigned managed identity works with an Azure VM
After the VM has an identity, use the service principal information to grant the VM access to Azure resources.
To call Azure Resource Manager, use role-based access control (RBAC) in Azure AD to assign the appropriate role to the VM service principal. To call Key Vault, grant your code access to the specific secret or key in Key Vault.
References:
https://docs.microsoft.com/en-us/azure/key-vault/quick-create-net
https://docs.microsoft.com/en-us/azure/active-directory/managed-identities-azure-resources/overview
NEW QUESTION 63
You have an Azure Sentinel workspace that has the following data connectors:
Azure Active Directory Identity Protection
Common Event Format (CEF)
Azure Firewall
You need to ensure that data is being ingested from each connector.
From the Logs query window, which table should you query for each connector? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 64
You are troubleshooting a security issue for an Azure Storage account.
You enable the diagnostic logs for the storage account.
What should you use to retrieve the diagnostics logs?
- A. Azure Storage Explorer
- B. Azure Security Center
- C. Azure Monitor
- D. the Security admin center
Answer: C
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/storage/blobs/monitor-blob-storage?tabs=azure-portal
NEW QUESTION 65
You have two Azure virtual machines in the East US2 region as shown in the following table.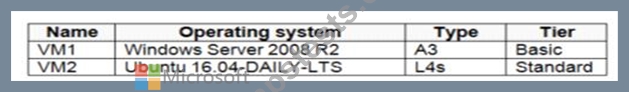
You deploy and configure an Azure Key vault.
You need to ensure that you can enable Azure Disk Encryption on VM1 and VM2.
What should you modify on each virtual machine? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure/virtual-machines/windows/generation-2#generation-1-vs-generation-2-capabilities
NEW QUESTION 66
You have an Azure subscription named Sub1.
In Azure Security Center, you have a workflow automation named WF1. WF1 is configured to send an email message to a user named User1.
You need to modify WF1 to send email messages to a distribution group named Alerts.
What should you use to modify WF1?
- A. Azure Application Insights
- B. Azure Logic Apps Designer
- C. Azure DevOps
- D. Azure Monitor
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/workflow-automation
https://docs.microsoft.com/en-us/learn/modules/resolve-threats-with-azure-security-center/6-exerciseconfigure-p
NEW QUESTION 67
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
Azure AD Privileged Identity Management (PIM) is enabled for the tenant.
In PIM, the Password Administrator role has the following settings:
Maximum activation duration (hours): 2
Send email notifying admins of activation: Disable
Require incident/request ticket number during activation: Disable
Require Azure Multi-Factor Authentication for activation: Enable
Require approval to activate this role: Enable
Selected approver: Group1
You assign users the Password Administrator role as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/bs-latn-ba/azure/active-directory/privileged-identity-management/pim-resource-roles-assign-roles
NEW QUESTION 68
You have an Azure subscription that contains a virtual machine named VM1.
You create an Azure key vault that has the following configurations:
* Name: Vault5
* Region: West US
* Resource group: RG1
You need to use Vault5 to enable Azure Disk Encryption on VM1. The solution must support backing up VM1 by using Azure Backup.
Which key vault settings should you configure?
- A. Secrets
- B. Access policies
- C. Locks
- D. Keys
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/key-vault/key-vault-secure-your-key-vault
NEW QUESTION 69
You create resources in an Azure subscription as shown in the following table.
VNET1 contains two subnets named Subnet1 and Subnet2. Subnet1 has a network ID of 10.0.0.0/24. Subnet2 has a network ID of 10.1.1.0/24.
Contoso1901 is configured as shown in the exhibit. (Click the Exhibit tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 70
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
You create and enforce an Azure AD Identity Protection user risk policy that has the following settings:
Assignment: Include Group1, Exclude Group2
Conditions: Sign-in risk of Medium and above
Access: Allow access, Require password change
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
http://www.rebeladmin.com/2018/09/step-step-guide-configure-risk-based-azure-conditional-access-policies/
NEW QUESTION 71
You have an Azure subscription. The subscription contains Azure virtual machines that run Windows Server 2016.
You need to implement a policy to ensure that each virtual machine has a custom antimalware virtual machine extension installed.
How should you complete the policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/azure/governance/policy/concepts/effects
NEW QUESTION 72
You have an Azure subscription named Sub1 that is associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
You plan to implement an application that will consist of the resources shown in the following table.
Users will authenticate by using their Azure AD user account and access the Cosmos DB account by using resource tokens.
You need to identify which tasks will be implemented in CosmosDB1 and WebApp1.
Which task should you identify for each resource? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
CosmosDB1: Create database users and generate resource tokens.
Azure Cosmos DB resource tokens provide a safe mechanism for allowing clients to read, write, and delete specific resources in an Azure Cosmos DB account according to the granted permissions.
WebApp1: Authenticate Azure AD users and relay resource tokens
A typical approach to requesting, generating, and delivering resource tokens to a mobile application is to use a resource token broker. The following diagram shows a high-level overview of how the sample application uses a resource token broker to manage access to the document database data:
References:
https://docs.microsoft.com/en-us/xamarin/xamarin-forms/data-cloud/cosmosdb/authentication
NEW QUESTION 73
You are configuring network connectivity for two Azure virtual networks named VNET1 and VNET2.
You need to implement VPN gateways for the virtual networks to meet the following requirements:
* VNET1 must have six site-to-site connections that use BGP.
* VNET2 must have 12 site-to-site connections that use BGP.
* Costs must be minimized.
Which VPN gateway SKI) should you use for each virtual network? To answer, drag the appropriate SKUs to the correct networks. Each SKU may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/azure/vpn-gateway/vpn-gateway-about-vpngateways#gwsku
NEW QUESTION 74
......
The Microsoft AZ-500 exam will equip you with the relevant skills to become a reputable security engineer with a focus on Azure.
Tested Material Used To AZ-500 Test Engine: https://www.dumpstests.com/AZ-500-latest-test-dumps.html
Steps Necessary To Pass The AZ-500 Exam: https://drive.google.com/open?id=1cZ1Gx4dOVYdLhTtPaDJCUVBnoBPD9XRp