

MD-102 Exam Questions - Real & Updated Questions PDF
Pass Guaranteed Quiz 2026 Realistic Verified Free Microsoft
Microsoft MD-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 179
You have the on-premises servers shown in the following table.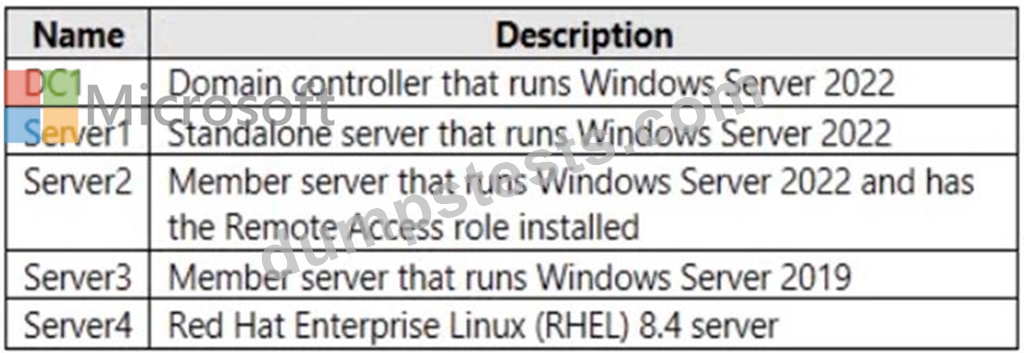
You have a Microsoft 365 E5 subscription that contains Android and iOS devices. All the devices are managed by using Microsoft Intune.
You need to implement Microsoft Tunnel for Intune. The solution must minimize the number of open firewall ports.
To which server can you deploy a Tunnel Gateway server, and which inbound ports should be allowed on the server to support Microsoft Tunnel connections? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.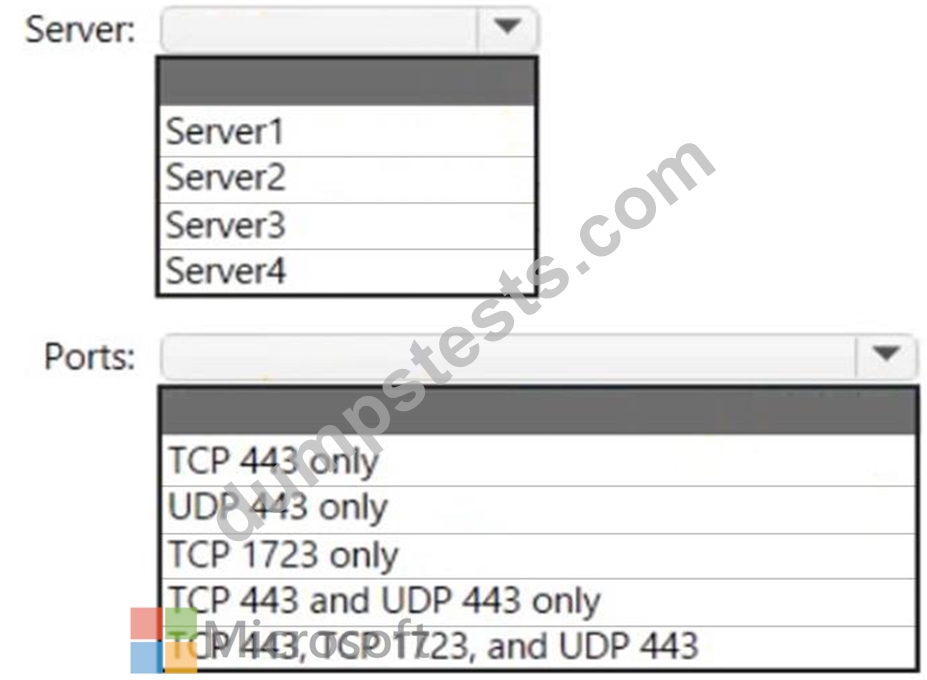
Answer:
Explanation: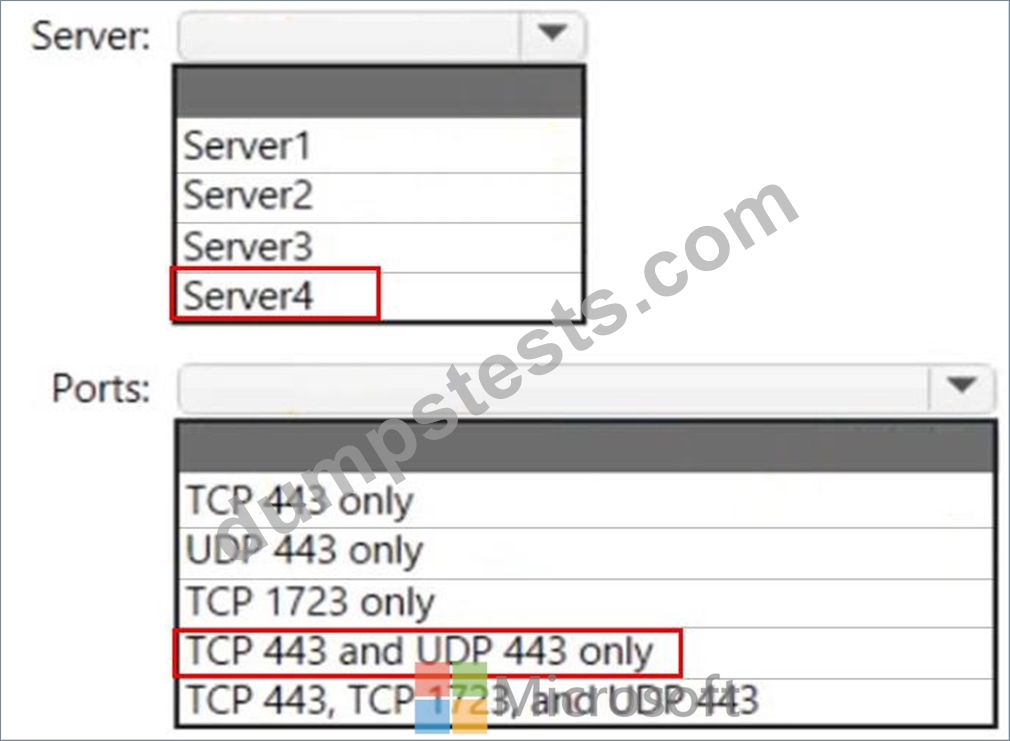
NEW QUESTION # 180
You have a Microsoft 365 E5 subscription. All devices are enrolled in Microsoft Intune.
You have a device group named Group1 that contains five Windows 11 devices.
You need to ensure that the devices in Group1 automatically receive new Windows 11 builds before the builds are released to the public.
What should you configure in Intune? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.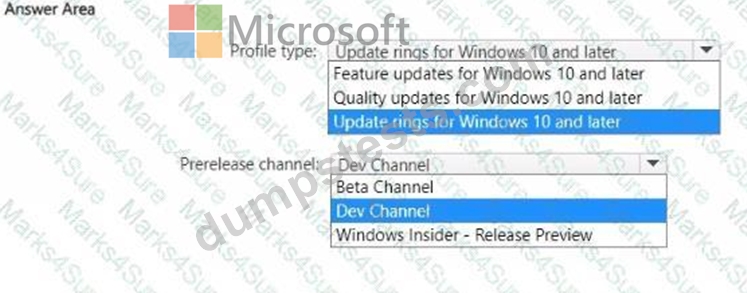
Answer:
Explanation: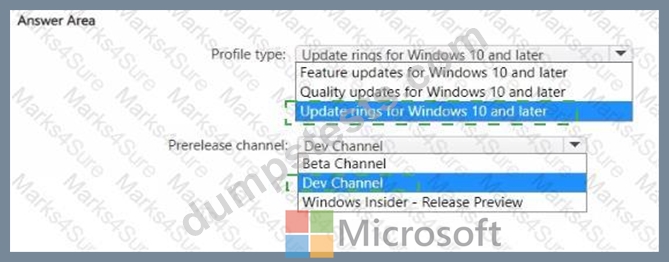
Explanation: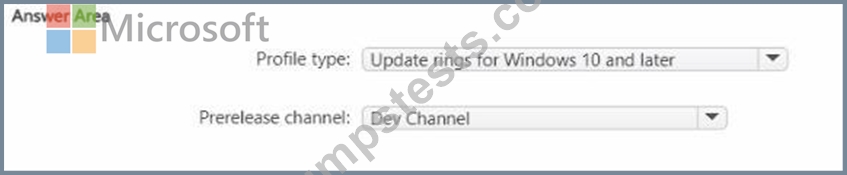
NEW QUESTION # 181
What is the maximum number of devices that User1 and User2 can enroll in Intune? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.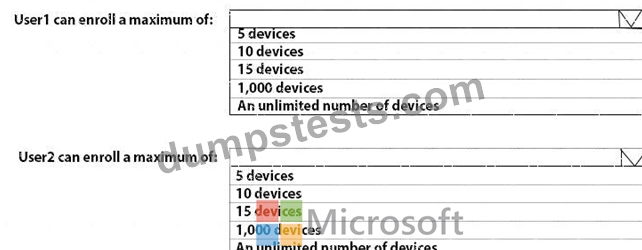
Answer:
Explanation: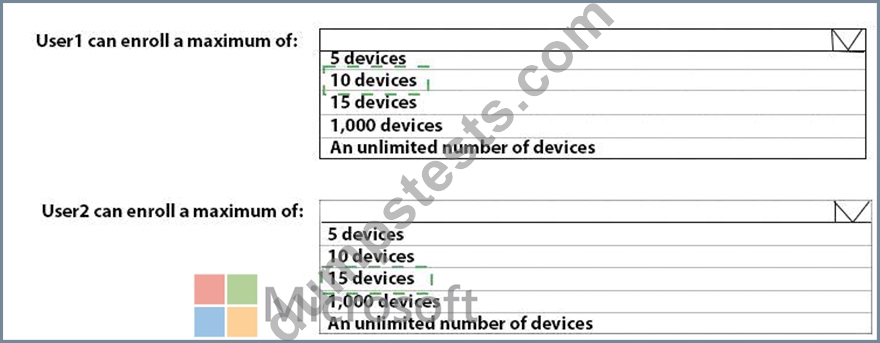
Explanation: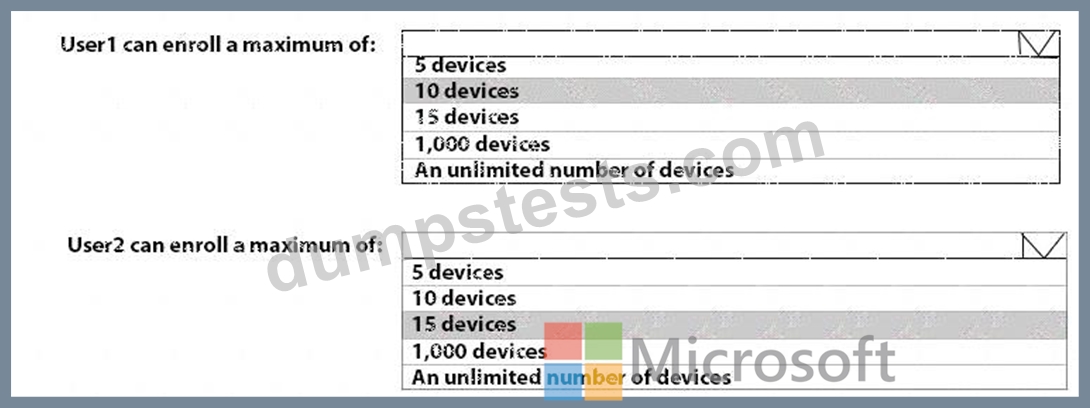
NEW QUESTION # 182
Your on-premises network contains an Active Directory domain that syncs with an Azure AD tenant. The tenant contains the groups shown in the following table.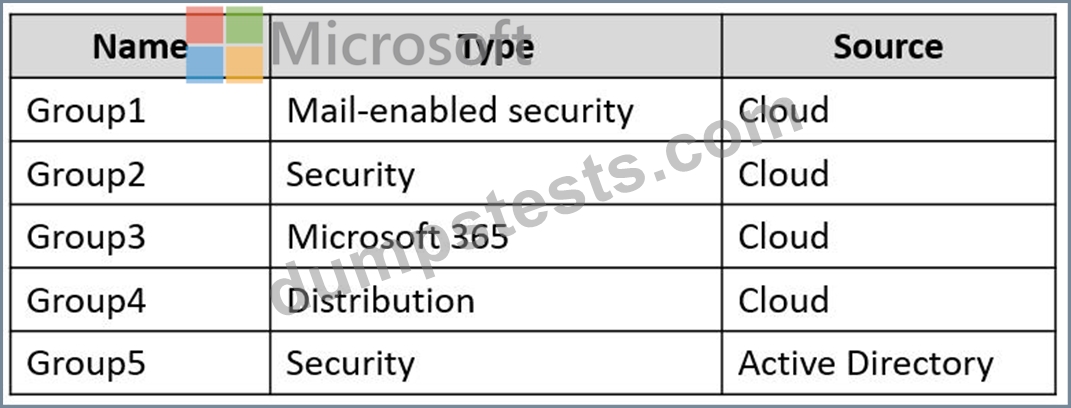
You plan to add new members to each group.
Which groups can you manage in the Azure Active Directory admin center?
- A. Group1, Group2, and Group3 only
- B. Group2 and Group3 only
- C. Group1, Group2, Group3, and Group4 only
- D. Group3 only
- E. Group1, Group2, Group3, and Group5 only
Answer: E
NEW QUESTION # 183
Case Study 2 - Contoso Ltd
Overview
Contoso, Ltd, is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
Contoso has the users and computers shown in the following table.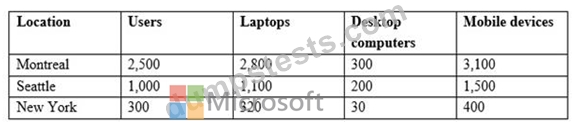
The company has IT, human resources (HR), legal (LEG), marketing (MKG) and finance (FIN) departments.
Contoso uses Microsoft Store for Business and recently purchased a Microsoft 365 subscription.
The company is opening a new branch office in Phoenix. Most of the users in the Phoenix office will work from home.
Existing Environment
The network contains an Active Directory domain named contoso.com that is synced to Microsoft Azure Active Directory (Azure AD).
All member servers run Windows Server 2016. All laptops and desktop computers run Windows
10 Enterprise.
The computers are managed by using Microsoft System Center Configuration Manager. The mobile devices are managed by using Microsoft Intune.
The naming convention for the computers is the department acronym, followed by a hyphen, and then four numbers, for example, FIN-6785. All the computers are joined to the on-premises Active Directory domain.
Each department has an organization unit (OU) that contains a child OU named Computers. Each computer account is in the Computers OU of its respective department.
Intune Configuration
The domain has the users shown in the following table.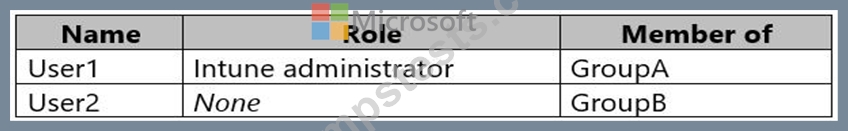
User2 is a device enrollment manager (DEM) in Intune.
The devices enrolled in Intune are shown in the following table.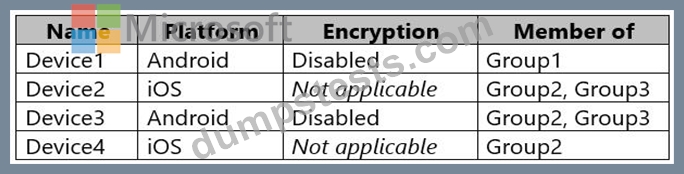
The device compliance policies in Intune are configured as shown in the following table.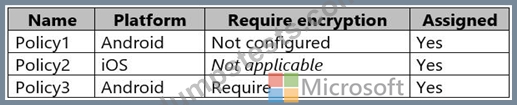
The device compliance policies have the assignments shown in the following table.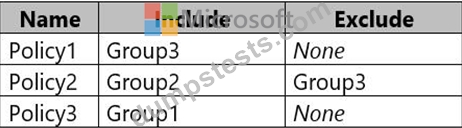
The device limit restrictions in Intune are configured as shown in the following table.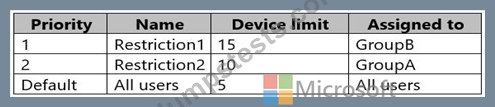
Requirements
Planned Changes
Contoso plans to implement the following changes:
- Provide new computers to the Phoenix office users. The new computers have Windows 10 Pro preinstalled and were purchased already.
- Start using a free Microsoft Store for Business app named App1.
- mplement co-management for the computers.
Technical Requirements
Contoso must meet the following technical requirements:
- Ensure that the users in a group named Group4 can only access Microsoft Exchange Online from devices that are enrolled in Intune.
- Deploy Windows 10 Enterprise to the computers of the Phoenix office users by using Windows Autopilot.
- Monitor the computers in the LEG department by using Windows Analytics.
- Create a provisioning package for new computers in the HR department.
- Block iOS devices from sending diagnostic and usage telemetry data.
- Use the principle of least privilege whenever possible.
- Enable the users in the MKG department to use App1.
- Pilot co-management for the IT department.
You need to meet the technical requirements for the IT department.
What should you do first?
- A. From the Configuration Manager console, add an Intune subscription.
- B. From the Microsoft Intune blade in the Azure portal, configure the Windows enrollment settings.
- C. From the Azure Active Directory blade in the Azure portal, enable Seamless single sign-on.
- D. From the Azure Active Directory blade in the Azure portal, configure the Mobility (MDM and MAM) settings.
Answer: D
Explanation:
MDM and MAM are not under Azure portal anymore. You have to go to Endpoint > Devices > Enroll devices | Windows enrollment > Automatic Enrollment.
https://docs.microsoft.com/en-us/sccm/comanage/tutorial-co-manage-clients
NEW QUESTION # 184
Your network contains an Active Directory domain named contoso.com. The domain contains two computers named Computer! and Computer2 that run Windows 10. On Computer1, you need to run the Invoke-Command cmdlet to execute several PowerShell commands on Computed. What should you do first?
- A. From Active Directory, configure the Trusted for Delegation setting for the computer account of Computed.
- B. On Computer1, run the HcK-PSSession cmdlet.
- C. On Computed, run the Enable-PSRemoting cmdlet.
- D. On Computed, add Computer! to the Remote Management Users group.
Answer: A
NEW QUESTION # 185
You have a Microsoft 365 tenant that uses Microsoft Intune to manage the devices shown in the following table.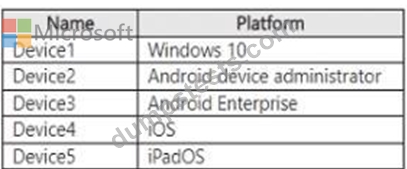
You need to deploy a compliance solution that meets the following requirements:
* Marks the devices as Not Compliant if they do not meet compliance policies
* Remotely locks noncompliant devices
What is the minimum number of compliance policies required, and which devices support the remote lock action? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.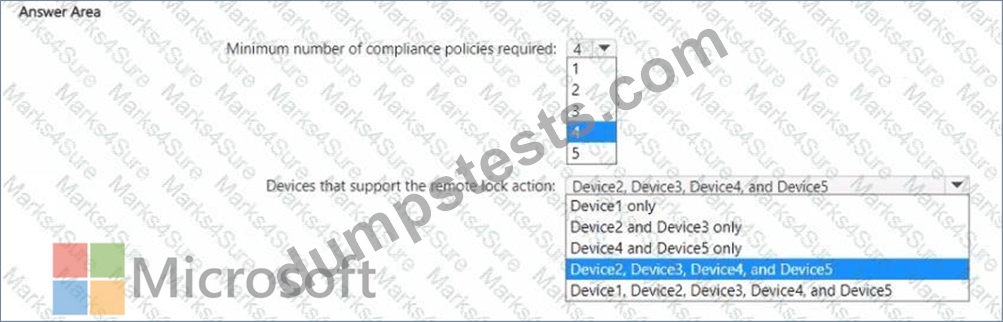
Answer:
Explanation: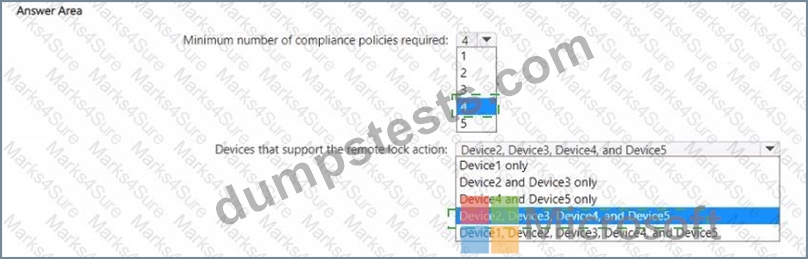
Explanation: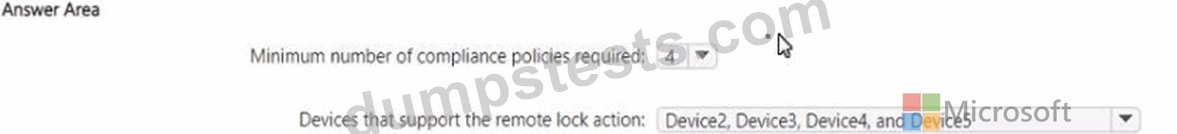
NEW QUESTION # 186
You need to meet the technical requirements for the new HR department computers.
How should you configure the provisioning package? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.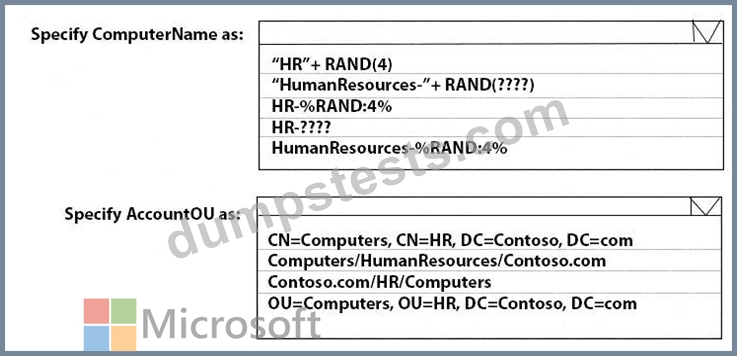
Answer:
Explanation: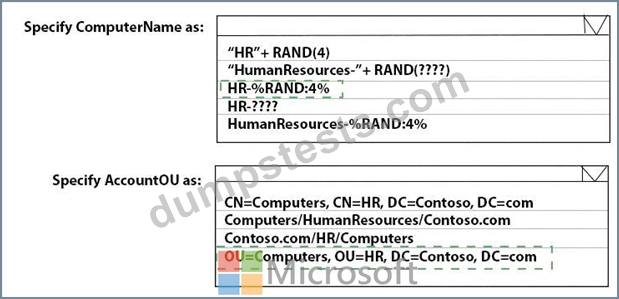
Explanation: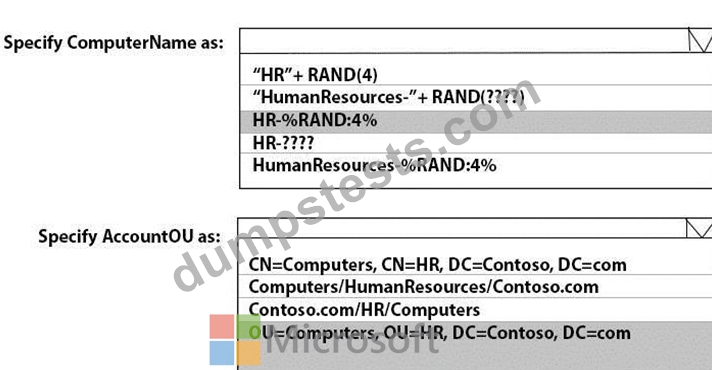
Reference:
https://docs.microsoft.com/en-us/windows/configuration/wcd/wcd-accounts
NEW QUESTION # 187
You have a Windows 11 capable device named Device1 that runs the 64-bit version of Windows 10 Enterprise and has Microsoft Office 2019 installed. You have the Windows 11 Enterprise images shown in the following table.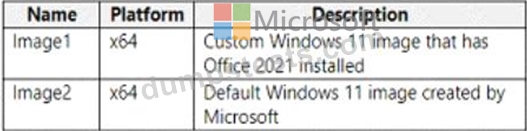
Which images can be used to perform an in-place upgrade of Device1?
- A. image1 only
- B. lmage2only
- C. Image1 and Image2
Answer: B
NEW QUESTION # 188
You have a Microsoft 365 E5 tenant that contains Windows devices enrolled in Microsoft Intune as shown in the following table.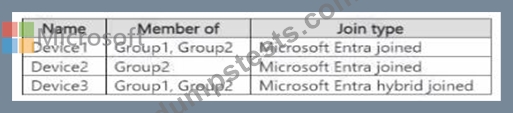
You create an Endpoint Privilege Management (EPM) elevation settings policy named ElevationSettmgsl that has the following settings:
* Endpoint Privilege Management: Enabled
o Default elevation response: Require user confirmation
o Validation: Business justification
* Assignments: Group1 Each device contains a file named File1.exe that can be run only by an administrator. You create an EPM elevation rules policy named ElevattonRules1 that has the following settings:
* Rule name: Rule1
o Elevation type: Automatic
o File name: Filel.exe
o File hash: <Filel.exe hash>
* Assignments: Group2
For each of the following statements, select Yes if the statement is true. Otherwise, select NOTE: Each correct selection is worth one point.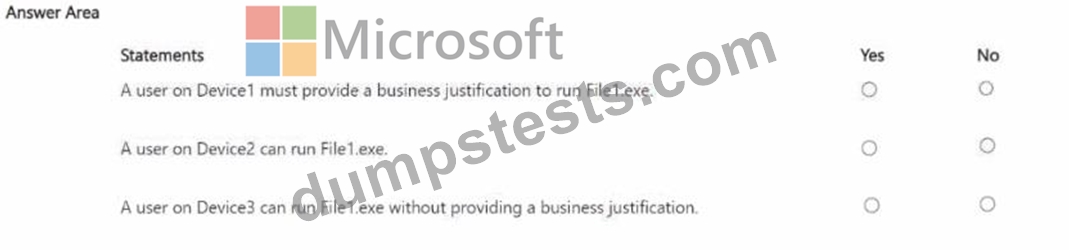
Answer:
Explanation: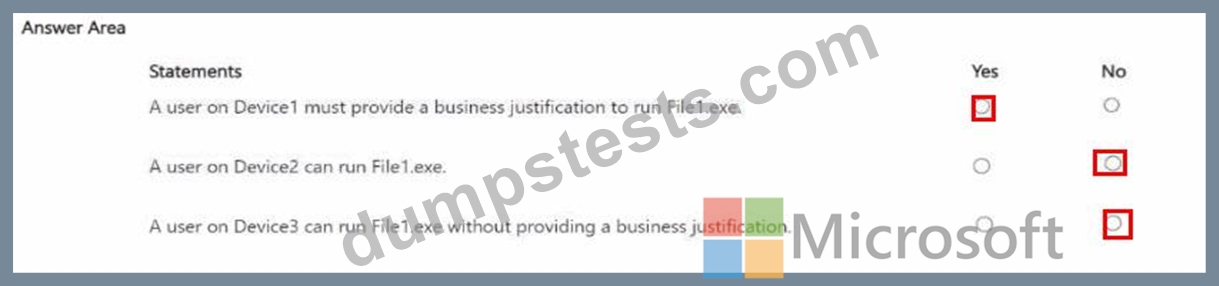
NEW QUESTION # 189
You have two computers that run Windows 10. The computers are enrolled in Microsoft Intune as shown in the following table.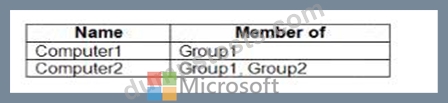
Windows 10 update rings are defined in Intune as shown in the following table.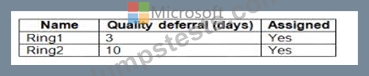
You assign the update rings as shown in the following table.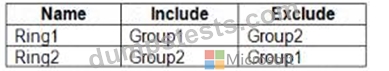
What is the effect of the configurations on Computer1 and Computer2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.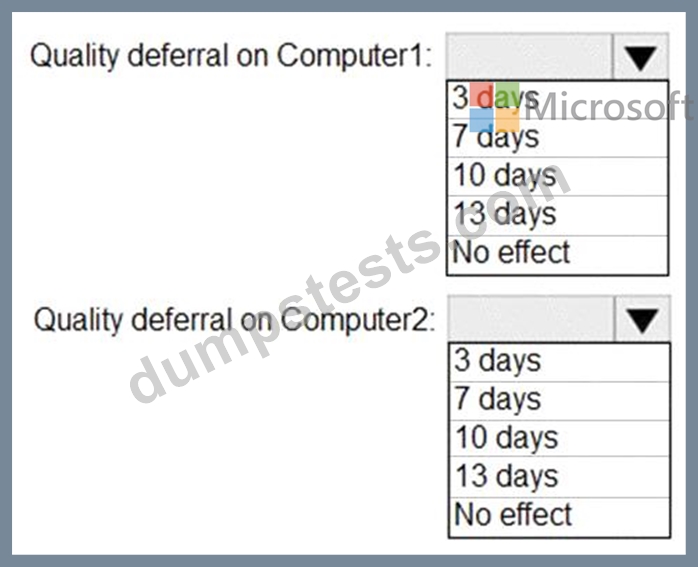
Answer:
Explanation: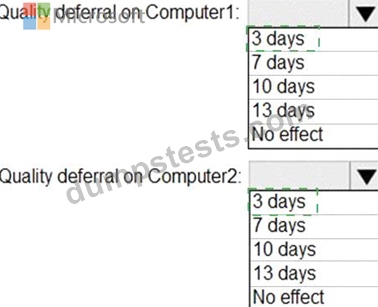
Explanation
A screenshot of a computer Description automatically generated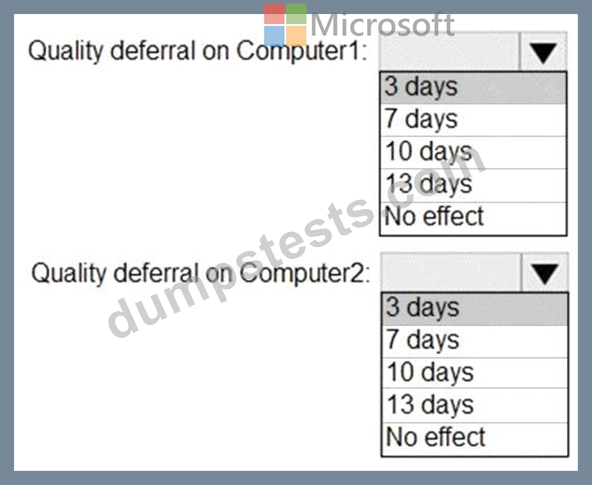
Computer1 and Computer2 are members of Group1. Ring1 is applied to Group1.
Note: The term "Exclude" is misleading. It means that the ring is not applied to that group, rather than that group being blocked.
References:
https://docs.microsoft.com/en-us/windows/deployment/update/waas-wufb-intune
https://allthingscloud.blog/configure-windows-update-business-using-microsoft-intune/
NEW QUESTION # 190
You implement the planned changes for Connection1 and Connection2
How many VPN connections will there be for User1 when the user signs in to Device 1 and Devke2? To answer select the appropriate options in the answer area.
NOTE; Each correct selection is worth one point.
Answer:
Explanation: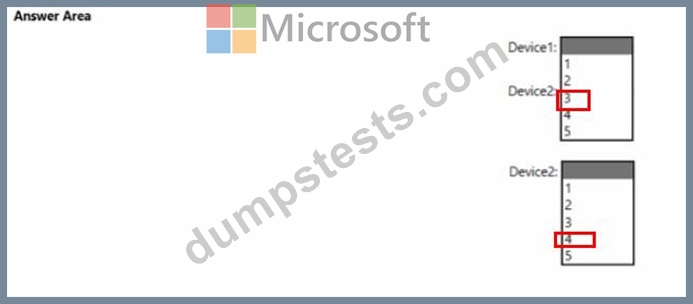
Topic 3, Contoso Ltd,
Overview
Contoso, Ltd, is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
Contoso has the users and computers shown in the following table.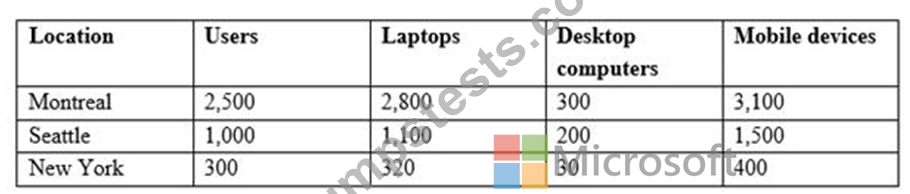
The company has IT, human resources (HR), legal (LEG), marketing (MKG) and finance (FIN) departments.
Contoso uses Microsoft Store for Business and recently purchased a Microsoft 365 subscription.
The company is opening a new branch office in Phoenix. Most of the users in the Phoenix office will work from home.
Existing Environment
The network contains an Active Directory domain named contoso.com that is synced to Microsoft Azure Active Directory (Azure AD).
All member servers run Windows Server 2016. All laptops and desktop computers run Windows 10 Enterprise.
The computers are managed by using Microsoft System Center Configuration Manager. The mobile devices are managed by using Microsoft Intune.
The naming convention for the computers is the department acronym, followed by a hyphen, and then four numbers, for example, FIN-6785. All the computers are joined to the on-premises Active Directory domain.
Each department has an organization unit (OU) that contains a child OU named Computers. Each computer account is in the Computers OU of its respective department.
Intune Configuration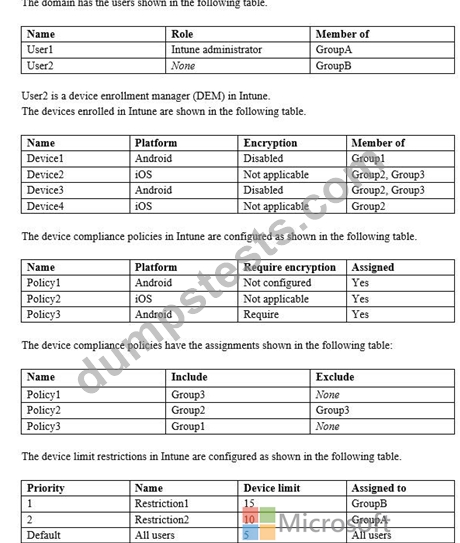
Requirements
Planned Changes
Contoso plans to implement the following changes:
Provide new computers to the Phoenix office users. The new computers have Windows 10 Pro preinstalled and were purchased already.
Start using a free Microsoft Store for Business app named App1.
Implement co-management for the computers.
Technical Requirements:
Contoso must meet the following technical requirements:
Ensure that the users in a group named Group4 can only access Microsoft Exchange Online from devices that are enrolled in Intune.
Deploy Windows 10 Enterprise to the computers of the Phoenix office users by using Windows Autopilot.
Monitor the computers in the LEG department by using Windows Analytics.
Create a provisioning package for new computers in the HR department.
Block iOS devices from sending diagnostic and usage telemetry data.
Use the principle of least privilege whenever possible.
Enable the users in the MKG department to use App1.
Pilot co-management for the IT department.
NEW QUESTION # 191
You have a Microsoft 365 E5 subscription that contains 150 hybrid Azure AD joined Windows devices. All the devices are enrolled in Microsoft Intune. You need to configure Delivery Optimization on the devices to meet the following requirements:
* Allow downloads from the internet and from other computers on the local network.
* Limit the percentage of used bandwidth to 50.
What should you use?
- A. a Windows Update for Business Group Policy setting
- B. a Microsoft Peer-to-Peer Networking Services Group Policy setting
- C. a configuration profile
- D. an Update ring for Windows 10 and later profile
Answer: C
Explanation:
A configuration profile is the correct answer because it allows you to configure Delivery Optimization settings for Windows devices in Intune. You can specify the download mode, bandwidth limit, caching options, and more. A configuration profile is a template that contains one or more settings that you can apply to groups of devices. Reference:
Windows 10 Delivery Optimization settings for Intune - Microsoft Intune | Microsoft Learn Delivery Optimization settings in Microsoft Intune
NEW QUESTION # 192
You need to capture the required information for the sales department computers to meet the technical requirements.
Which Windows PowerShell command should you run first?
- A. Install-Script Get-WindowsAutoPilotInfo
- B. Install-Module WindowsAutoPilotIntune
- C. Get-WindowsAutoPilotInfo
- D. Import-AutoPilotCSV
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/windows/deployment/windows-autopilot/existing-devices
"This topic describes how to convert Windows 7 or Windows 8.1 domain-joined computers to Windows 10 devices joined to either Azure Active Directory or Active Directory (Hybrid Azure AD Join) by using Windows Autopilot"
Topic 2, Case Study Contoso, Ltd.Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
Contoso has a Microsoft 365 E5 subscription.
Network Environment
The network contains an on-premises Active domain named Contoso.com. The domain contains the servers shown in the following table.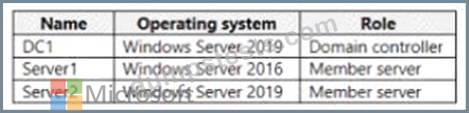
Contoso has a hybrid Azure Active Directory (Azure AD) tenant named Contoso.com.
Contoso has a Microsoft Store for Business instance.
Users and Groups
The Contoso.com tenant contains the users shown in the following table.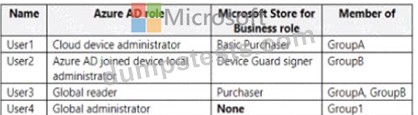
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group and Group have a Membership type of Assign
Devices
Contoso has the Windows 10 devices shown in the following table.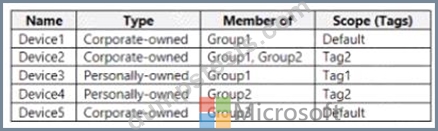
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft intune.
The Windows 10 devices are configured as shown in the following table.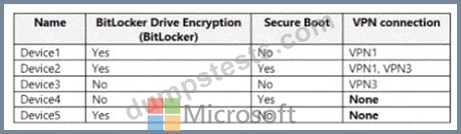
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder 1.
Microsoft Endpoint Manager Configuration
Microsoft Endpoint Manager has the compliance policies shown in the following table.
The Compliance policy settings are shown in the following exhibit.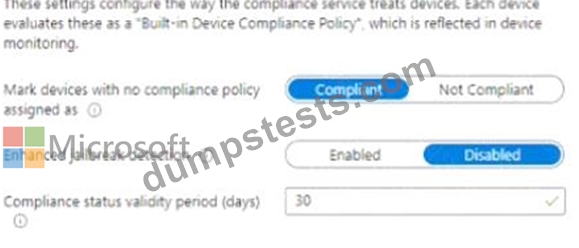
The Automatic Enrolment settings have the following configurations:
* MDM user scope GroupA
* MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
* Name: Protection1
* Folder protection: Enable
* List of apps that have access to protected folders: CV\AppA.exe
* List of additional folders that need to be protected: D:\Folderi1
* Assignments
Windows Autopilot Configuration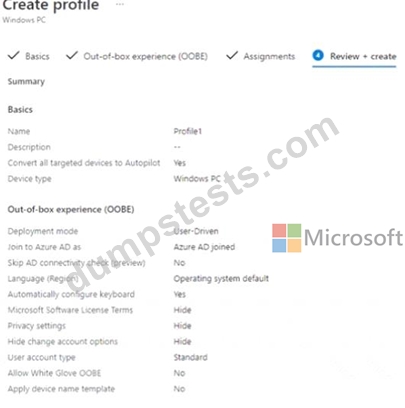
Currently, there are no devices deployed by using Window Autopilot
The Intune connector tor Active Directory is installed on Server 1.
Planned Changes
Contoso plans to implement the following changes:
* Purchase a new Windows 10 device named Device6 and enroll the device in Intune.
* New computers will be deployed by using Windows Autopilot and will be hybrid Azure AO joined.
* Deploy a network boundary configuration profile that will have the following settings:
* Name Boundary 1
* Network boundary 192.168.1.0/24
* Scope tags: Tag 1
* Assignments;
* included groups: Group 1. Group2
* Deploy two VPN configuration profiles named Connection! and Connection that will have the following settings:
* Name: Connection 1
* Connection name: VPNI
* Connection type: L2TP
* Assignments:
* Included groups: Group1. Group2, GroupA
* Excluded groups: -
* Name: Connection
* Connection name: VPN2
* Connection type: IKEv2 i Assignments:
* included groups: GroupA
* Excluded groups: GroupB
* Purchase an app named App1 that is available in Microsoft Store for Business and to assign the app to all the users.
Technical Requirements
Contoso must meet the following technical requirements:
* Users in GroupA must be able to deploy new computers.
* Administrative effort must be minimized.
NEW QUESTION # 193
You manage 1.000 devices by using Microsoft Intune. You review the Device compliance trends report. For how long will the report display trend data?
- A. 60 days
- B. 90 days
- C. 365 days
- D. 30 days
Answer: A
NEW QUESTION # 194
You have 100 computers that run Windows 10.
You plan to deploy Windows 11 to the computers by performing a wipe and load installation.
You need to recommend a method to retain the user settings and the user data.
Which three actions should you recommend be performed in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.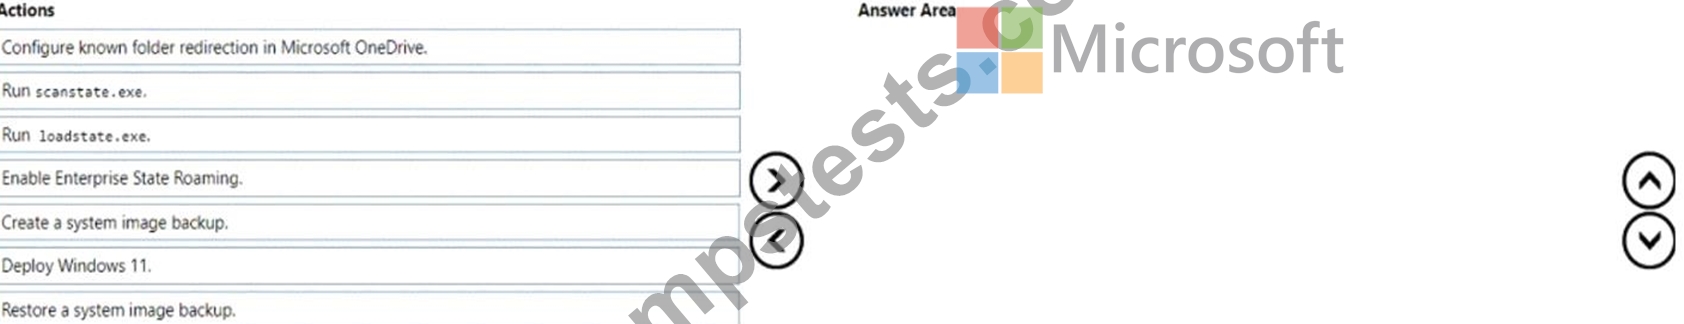
Answer:
Explanation: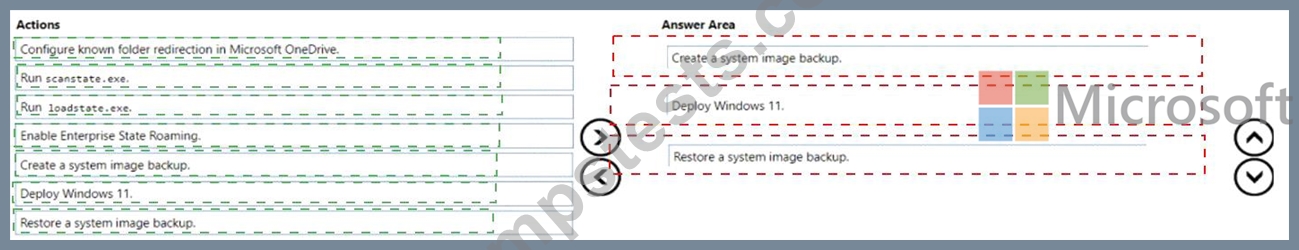
Explanation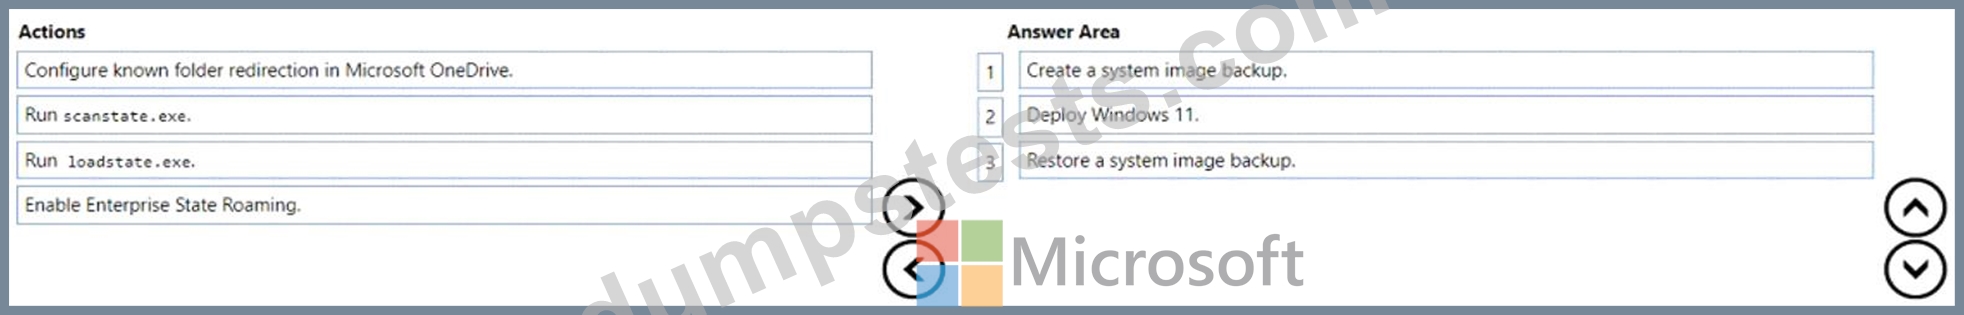
NEW QUESTION # 195
Hotspot Question
You have a Microsoft 365 subscription.
You use Microsoft Intune Suite to manage devices.
You have the iOS app protection policy shown in the following exhibit.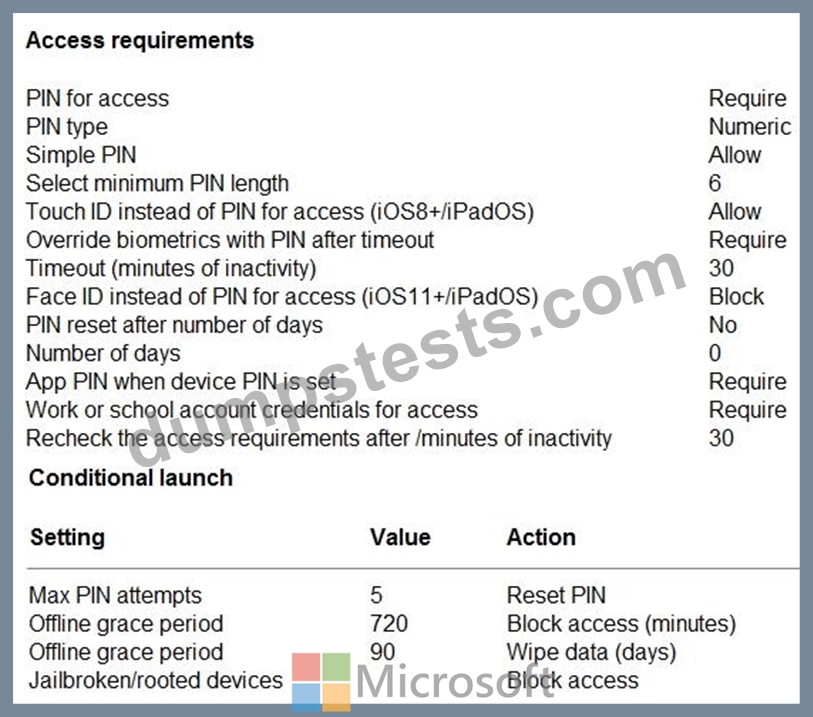
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic. NOTE: Each correct selection is worth one point.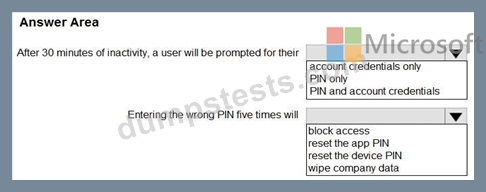
Answer:
Explanation: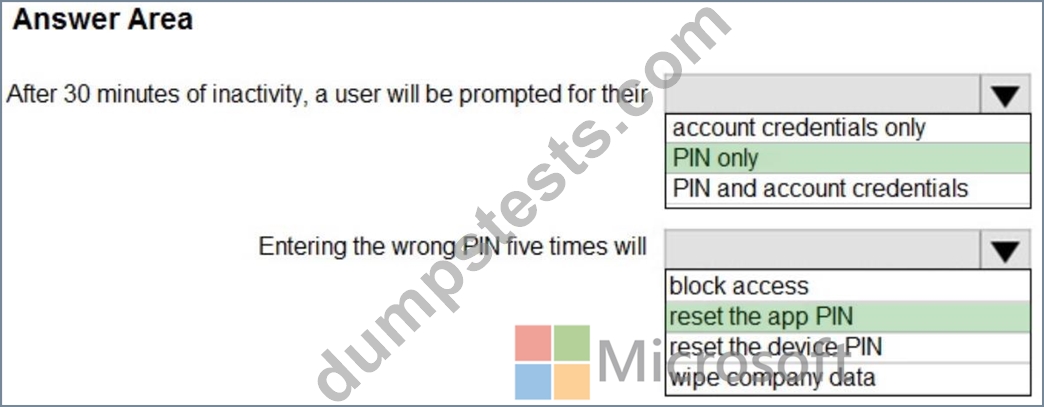
NEW QUESTION # 196
Drag and Drop Question
You have a Microsoft 365 subscription that contains two users named User1 and User2.
You need to ensure that the users can perform the following tasks:
- User1 must be able to create groups and manage users.
- User2 must be able to reset passwords for nonadministrative users.
The solution must use the principle of least privilege.
Which role should you assign to each user? To answer, drag the appropriate roles to the correct users. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.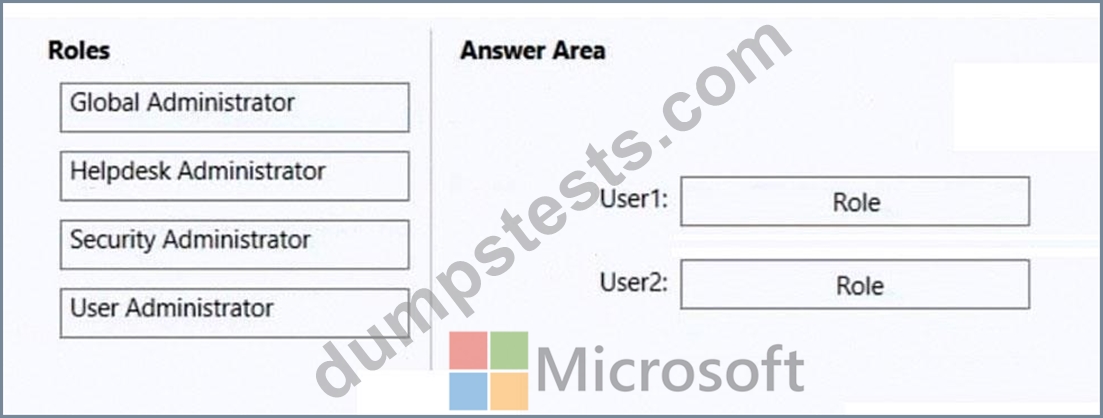
Answer:
Explanation: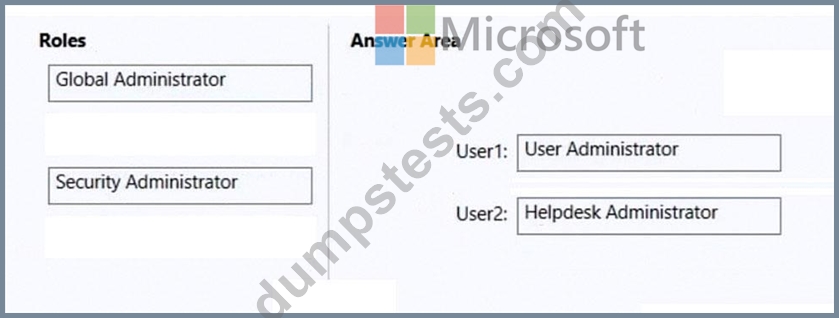
Explanation:
Box 1: User Administrator
User admin
Assign the user admin role to users who you want to access and manage user password resets and manage users and groups. They can also open and manage support requests to Microsoft support.
Box 2: Helpdesk Administrator
Assign the Helpdesk admin role to users who want to reset passwords, force users to sign out for any security issues. They can also open and manage support requests to Microsoft support. The Helpdesk admin can only help non-admin users and users assigned these roles: Directory reader, Guest inviter, Helpdesk admin, Message center reader, and Reports reader.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/admin/add-users/admin-roles-page
NEW QUESTION # 197
You have a Microsoft 365 tenant that contains the Windows 10 devices shown in the following table.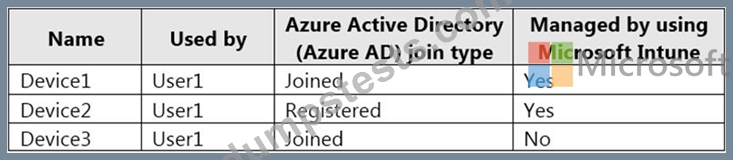
You enable Enterprise State Roaming.
You need to ensure that User1 can sync Windows settings across the devices.
What should you do?
- A. Add a Microsoft account to each device.
- B. Enroll Device3 in Intune.
- C. Join Device2 to Azure AD.
- D. Remove Device1 and Device2 from Intune.
Answer: C
Explanation:
For a Windows 10 or newer device to use the Enterprise State Roaming service, the device must authenticate using an Azure AD identity. For devices that are joined to Azure AD, the user's primary sign-in identity is their Azure AD identity, so no other configuration is required.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/devices/enterprise-state-roaming-enable
NEW QUESTION # 198
You have a Microsoft 365 E5 subscription.
All devices are enrolled in Microsoft Intune.
You need to ensure that devices that have NOT checked in for 30 days are deleted from intune.
What should you configure from the Microsoft Intune admin center?
- A. a device limit restriction
- B. a device clean-up rule
- C. a configuration profile
- D. automatic enrollment
Answer: B
NEW QUESTION # 199
......
Get to the Top with MD-102 Practice Exam Questions: https://www.dumpstests.com/MD-102-latest-test-dumps.html
Free Microsoft 365 Certified MD-102 Ultimate Study Guide: https://drive.google.com/open?id=1etwOtuhEeHi1MrteLi-YkJUgwR6DiukZ